 exam
Cisco 300-220 is easier to misunderstand than it is to describe. The current 300-220 CBRTHD exam, Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity, is a 90-minute Cisco professional-level concentration exam. Passing it earns the Cisco Certified Cybersecurity Specialist – Threat Hunting and Defending credential and can also satisfy the concentration requirement for CCNP Cybersecurity.
The harder question is not what the exam is called. It is what you should actually be comfortable doing before you sit for it.
The exam brings together threat modeling, threat actor attribution, threat hunting techniques, hunting processes, and hunting outcomes. These make more sense as parts of the same security scenario than as isolated subjects. Cisco’s current training also emphasizes proactive searches across networks, endpoints, and datasets for malicious, suspicious, or risky activity that existing controls may have missed.
That is the mindset worth bringing into your preparation.
What 300-220 Actually Requires From You
The exam is about connecting cybersecurity evidence
It is easy to approach 300-220 as a collection of subjects: study threat intelligence, review MITRE ATT&CK, learn threat modeling, understand attribution, then work through practice questions.
That looks organized, but it can create a false sense of readiness.
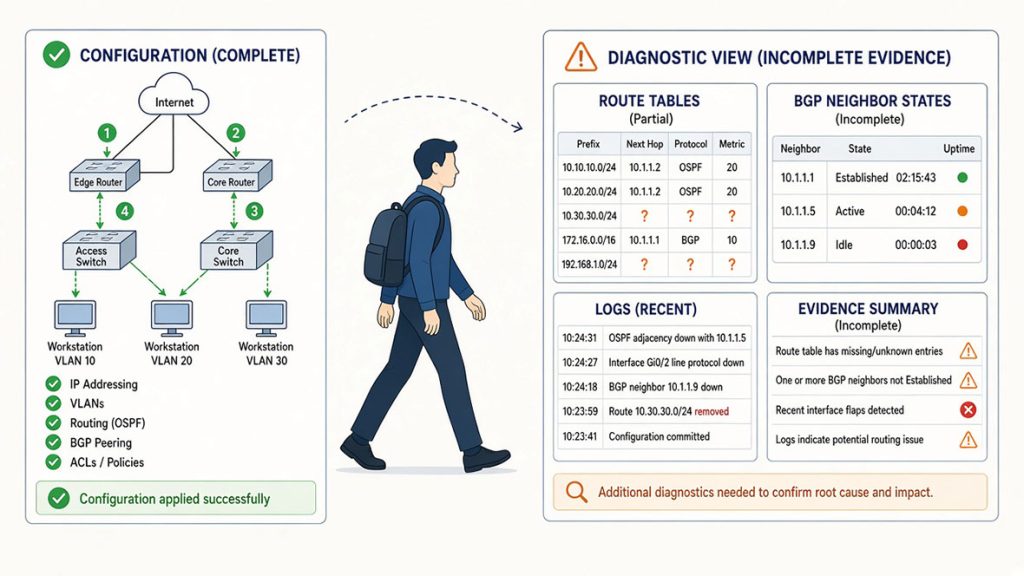
A more useful way to look at the exam is through a threat-hunting scenario. You may have endpoint information, network behavior, threat intelligence, or several types of evidence at once. The real challenge is understanding what that information means, how the pieces relate, and what a reasonable hunting approach would look like.
In other words, you are building the ability to move between evidence, hypotheses, hunting methods, technologies, and conclusions.
Knowing terminology is only the starting point
This is where many study plans become too comfortable. You read about MITRE ATT&CK, recognize SIEM and endpoint telemetry, learn common threat-hunting terminology, and feel productive because everything starts to look familiar.
Recognition is not the same as understanding.
Knowing what an indicator of compromise means does not automatically tell you how much weight to give it in a particular scenario. The same applies to SIEM, endpoint telemetry, network telemetry, threat intelligence, and attribution.
Cisco’s CBRTHD training takes a practical approach to hunting across networks, endpoints, and datasets, including Cisco and third-party security platforms.
The preparation lesson is simple: focus on interpreting security situations, not just recognizing security terms.
The Hard Part Is Connecting the Pieces
Threat intelligence, modeling, hunting, and attribution belong in the same picture
One of the easiest mistakes with 300-220 preparation is treating every objective as a separate subject.
Threat intelligence becomes one study session. Threat modeling gets another. MITRE ATT&CK becomes another. Attribution becomes a vocabulary exercise.
Threat hunting does not work that way.
A hunter may start with intelligence or a hypothesis, examine endpoint or network evidence, compare observed behavior with known techniques, and determine what the evidence actually supports. Attribution may be part of that analysis, but the evidence still determines how far the conclusion can reasonably go.
You do not need to turn this into a complicated methodology exercise. You simply need to recognize that the concepts interact.
Cisco technologies matter because they provide context
The exam title includes using Cisco Technologies for Cybersecurity, so that part should remain visible in your preparation.
Cisco’s current CBRTHD training covers hunting across networks, endpoints, and datasets and includes Cisco and third-party security platforms. The material also references network traffic, endpoint data, Windows event information, SIEM-based hunting, and Cisco security technologies.
The point is not to memorize a product catalog.
It is to understand the role security technology plays inside a hunting scenario. When a question presents endpoint evidence, network information, or data from a security platform, you should understand why that evidence matters and how it contributes to the investigation.
What Should You Know Before You Start Studying?
Existing security experience can change the learning curve
Cisco does not require a prerequisite for the 300-220 concentration itself, but candidates do not all start from the same place. Cisco’s current CCNP Cybersecurity information lists 300-220 as one of the concentration choices alongside the 350-201 core exam.
If you already work with cybersecurity operations, network security, SIEM platforms, endpoint telemetry, threat intelligence, or security investigations, many of the relationships between the topics may feel more familiar.
If those concepts are new to you, you first need enough context to understand what the evidence represents before practice questions become particularly useful.
Otherwise, it is easy to learn why an answer is correct without understanding the security situation behind it.
A practical sequence is simple: establish the concept, work through scenarios, identify where your reasoning breaks down, then review that area again.
Your preparation should expose uncertainty
A better test than counting study hours is this:
When you encounter a 300-220 scenario, can you explain why one answer makes more sense than another?
If you consistently choose the correct answer but cannot explain the reasoning, there is still a gap. If you understand the scenario but regularly hesitate between two options, that hesitation is useful information.
It tells you where another review is needed.
What I Would Focus on Before Booking the Exam
Look for scenario comfort, not just topic coverage
Before scheduling 300-220, pay attention to how comfortably you can work through security scenarios.
You should be able to interpret common threat-hunting situations, distinguish between different types of evidence, and understand how security technologies contribute to an investigation. When two options seem plausible, you should be able to explain why one fits the scenario better.
That matters more than simply recognizing a long list of terms.
Do not let the blueprint become your entire study strategy
The official exam topics are the right starting point because they define the current scope. But reading the blueprint repeatedly is not the same as preparing.
Use it as a map, then build understanding underneath it.
If the topic is threat actor attribution, for example, do not stop at defining attribution. Think about what evidence could support a conclusion and how confidently that conclusion could be made.
That small shift makes the official topic list much more useful.
Why Practice Questions Still Matter
Practice questions have a legitimate role in 300-220 preparation.
They can make question wording more familiar, reveal weak areas, help you practise decisions under time pressure, and show whether you understand an explanation or simply recognize an answer.
Cisco also includes practice tests within its broader Cisco U. learning approach as a way to check readiness and practise answering questions before the actual exam.
The difference is what happens after you answer.
Question → answer → explanation → identify the gap → review → practise again.
The goal is not to accumulate completed questions. It is to use them as feedback about your understanding.
That also means paying attention to hesitation. If you select the correct answer only after eliminating several alternatives, the question may still have exposed uncertainty. Those moments are worth reviewing because they show where your understanding is not yet automatic.
Choosing a 300-220 Preparation Resource
Match the resource to the way you actually study
Preparation does not need to become complicated.
A useful 300-220 preparation resource should fit your study routine and make review practical. For some candidates, that means a structured PDF. For others, an online testing environment makes more sense. Having access to both can be useful at different stages.
The practical features matter most. You should be able to review questions, check answers, revisit difficult items, and practise under timed conditions when you are ready.
Leads4Pass currently lists 300-220 Conducting Threat Hunting and Defending using Cisco Technologies for Cybersecurity among its exam preparation materials, with 133 Q&A shown on its current site. The preparation platform provides PDF and Web TestEngine study options, with interactive practice, incorrect-question review, marked questions, and timed mock exams available through the Web TestEngine.
Practice format can affect your review
PDF and online practice serve different purposes.
A PDF can work well when you want to review questions and explanations in a structured way. An interactive test environment is useful when you want to simulate an exam session, track incorrect answers, or revisit marked questions.
There is no need to force one format into every stage of preparation. Detailed review may matter more early on, while timed practice can become more useful closer to the exam.
A Practical Option for 300-220 Candidates
Leads4Pass can fit into the practice stage
Once you have reviewed the current Cisco exam scope and built enough foundational knowledge to understand the subject, a dedicated question resource can become part of the practice phase.
The current Leads4Pass site lists its 300-220 material as a 133-Q&A preparation resource and provides PDF and Web TestEngine formats for exam practice.
Leads4Pass 300-220 preparation page
The useful part is being able to turn practice into a feedback loop. If certain scenarios
repeatedly expose uncertainty around threat modeling, evidence interpretation, attribution, or hunting processes, you have a clear direction for further review.
What Current Candidate Discussions Tell You
Resource availability has been a real preparation issue
Community discussions are useful, but they need to be read in context.
A Reddit discussion from 2025 shows candidates looking for CBRTHD study resources and discussing options such as Cisco U., instructor-led training, and independent threat-hunting material. It does not represent every candidate or every current exam experience, but it does reflect a practical reality: finding preparation resources has been part of the challenge for people approaching this exam.
That makes choosing a study format that fits your own preparation routine more relevant than simply collecting more resources.
Community discussions can help you understand preparation experiences and resource availability. Cisco remains the appropriate source for current exam scope and official certification information.
The Readiness Question I Would Actually Ask
Can you reason through the scenario without relying on recognition?
Take a 300-220 scenario and explain what you think is happening. Identify the evidence that matters, consider what could change your interpretation, and decide which hunting approach or security technology fits the situation.
If you can do that consistently, your preparation is moving in the right direction.
If your reasoning becomes uncertain when the wording changes, keep working on the underlying concepts.
That is where practice becomes useful: it shows you what you understand and what still needs attention.
Final Judgment
If you are preparing for Cisco 300-220, do not measure readiness by the number of answers you recognize. Measure it by how confidently you can work through the type of cybersecurity scenario the exam is built around.
Use the official scope for direction, technical study for understanding, and practice questions to test that understanding.
For candidates looking for a focused 300-220 practice resource, the current Leads4Pass page provides dedicated Q&A material with PDF and Web TestEngine study formats.

 Kyle Bray
Recent Comments